
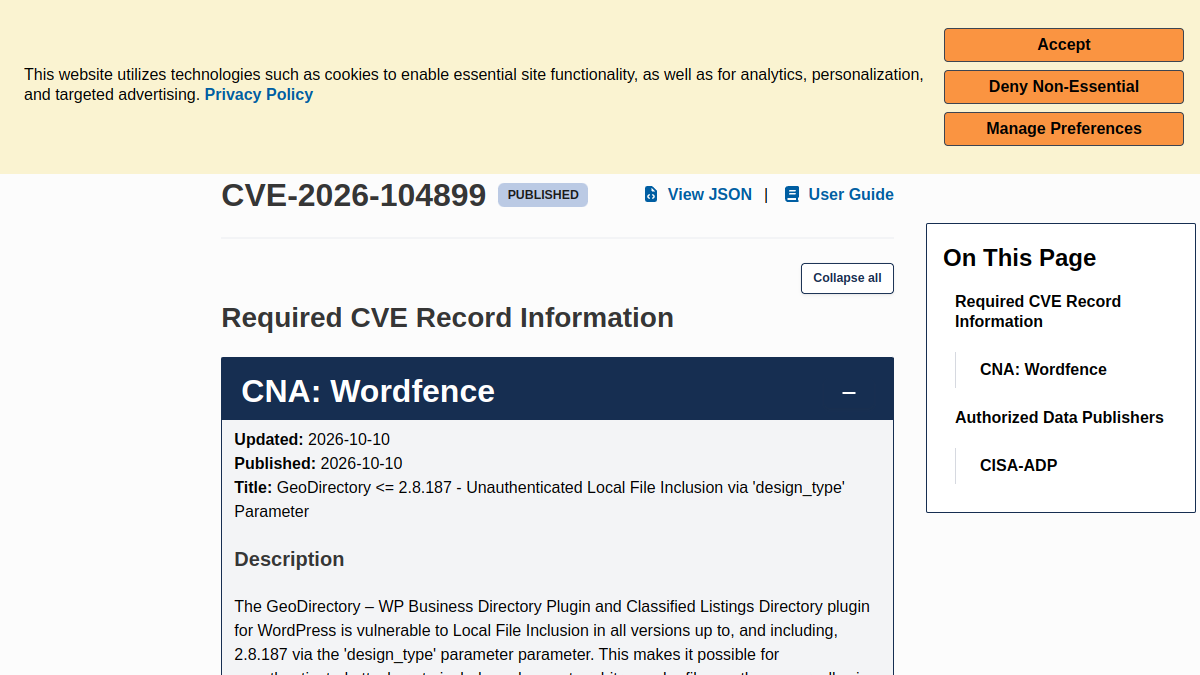
| CVE ID | CVE-2026-104899 |
| Severity | HIGH — CVSS CVSS V3.1 8.1 |
| Vector | CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H |
| CWE | CWE-98 CWE-98 Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') |
| Produk | paoltaia / GeoDirectory – WP Business Directory Plugin and Classified Listings Directory — 0 (affected) |
| Dipublikasikan | 2026-10-10 |
Ringkasan Cepat
- CVE-2026-104899 adalah kerentanan Local File Inclusion pada plugin WordPress GeoDirectory versi hingga dan termasuk 2.8.187.
- Penyerang tanpa autentikasi dapat menyertakan dan mengeksekusi file .php arbitrer karena nonce geodir_basic_nonce tersedia di setiap halaman frontend publik.
- Severity HIGH 8.1 (CVSS v3.1) dengan dampak tinggi pada kerahasiaan, integritas, dan ketersediaan.
Ringkasan Kerentanan
CVE-2026-104899 adalah kerentanan Local File Inclusion (LFI) pada plugin WordPress GeoDirectory – WP Business Directory Plugin and Classified Listings Directory. Menurut deskripsi resmi, seluruh versi hingga dan termasuk 2.8.187 rentan melalui parameter design_type.
Penyerang tanpa autentikasi dapat menyertakan dan mengeksekusi file .php arbitrer di server. Nonce yang dibutuhkan, geodir_basic_nonce, tersedia untuk setiap pengunjung anonim karena dilokalkan ke setiap halaman frontend publik melalui objek skrip geodir_params. Artinya, tidak diperlukan autentikasi, interaksi pengguna, atau konten situs tertentu untuk mengeksploitasi kerentanan ini.
Severity: HIGH 8.1 (CVSS v3.1) dengan vektor CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H. Kategori CWE: CWE-98.
Dampak Teknis
Kerentanan ini memungkinkan file .php lokal disertakan dan dieksekusi. Dampaknya mencakup eksekusi kode PHP apa pun yang ada di dalam file tersebut. Penyerang dapat memanfaatkannya untuk melewati kontrol akses, memperoleh data sensitif, atau mencapai eksekusi kode jika file .php dapat diunggah dan disertakan.
Vektor CVSS menunjukkan dampak tinggi pada kerahasiaan, integritas, dan ketersediaan (C:H/I:H/A:H). Meskipun nilai AC:H menunjukkan kompleksitas serangan yang tinggi, kombinasi tanpa autentikasi (PR:N) dan tanpa interaksi pengguna (UI:N) tetap menjadikannya risiko serius.
Produk Terdampak
Produk yang terdampak adalah plugin WordPress dari vendor paoltaia: GeoDirectory – WP Business Directory Plugin and Classified Listings Directory. Berdasarkan judul CNA, semua versi hingga dan termasuk 2.8.187 terpengaruh.
Kerentanan ini bersifat unauthenticated. Tidak ada kebutuhan akun pengguna, peran tertentu, atau konten khusus. Karena nonce tersedia di halaman frontend publik, permukaan serangan menjadi lebih luas bagi situs yang menjalankan plugin ini.
Konteks dan Referensi
Publikasi CVE: 2026-10-10T05:31:02.786Z. Referensi resmi mencakup Wordfence Threat Intel, beberapa tautan kode di Plugins Trac, dan commit perbaikan di GitHub AyeCode/geodirectory.
Dari perspektif pertahanan, kerentanan ini menegaskan pentingnya manajemen patch, pembatasan eksekusi file di direktori unggahan, serta pemantauan log untuk parameter atau pola permintaan yang tidak wajar. Jangan mengandalkan nonce yang terekspos ke publik sebagai kontrol keamanan tunggal.
Mitigasi dan Perbaikan
- Segera perbarui plugin GeoDirectory ke versi yang lebih baru setelah vendor merilis perbaikan. Pantau repositori resmi dan commit GitHub AyeCode/geodirectory (2357d640dad7973988742a6706b3a857b6b05d52) untuk ketersediaan patch.
- Jika pembaruan belum tersedia, pertimbangkan menonaktifkan sementara plugin GeoDirectory hingga patch diterapkan.
- Jangan mengandalkan nonce geodir_basic_nonce sebagai kontrol keamanan karena nilai tersebut tersedia bagi setiap pengunjung anonim di halaman frontend publik.
- Terapkan aturan WAF atau pembatasan akses untuk mendeteksi dan memblokir permintaan mencurigakan yang memanfaatkan parameter design_type, serta tinjau log server untuk indikasi upaya include file lokal.
- Lakukan audit file .php yang dapat diunggah dan dipanggil oleh aplikasi; batasi izin tulis dan eksekusi pada direktori unggahan.
Referensi Resmi
- CVE-2026-104899 — CVE Program (cve.org)
- https://www.wordfence.com/threat-intel/vulnerabilities/id/ac817587-1403-46e2-84bf-be5fcadc5425?source=cve
- https://plugins.trac.wordpress.org/browser/geodirectory/tags/2.8.187/includes/widgets/class-geodir-widget-tags.php#L1064
- https://plugins.trac.wordpress.org/browser/geodirectory/tags/2.8.187/includes/class-geodir-ajax.php#L709
- https://plugins.trac.wordpress.org/browser/geodirectory/tags/2.8.187/includes/template-functions.php#L143
- https://plugins.trac.wordpress.org/browser/geodirectory/tags/2.8.187/includes/template-functions.php#L199
- https://github.com/AyeCode/geodirectory/commit/2357d640dad7973988742a6706b3a857b6b05d52
Artikel ini disusun dari data publik CVE Program (cve.org). Selalu verifikasi patch resmi dari vendor sebelum menerapkan perubahan.
Pertanyaan yang Sering Diajukan (FAQ)
Apa itu CVE-2026-104899?
Versi GeoDirectory mana yang terdampak?
Apakah perlu autentikasi untuk mengeksploitasi kerentanan ini?
Seberapa parah dampaknya?
Apakah sudah ada patch resmi?
Apa yang harus dilakukan administrator situs?
English Version — ": "CVE-2026-104899: Unauthenticated GeoDirectory LFI",
Quick Summary
- ": "- CVE-2026-104899 is a Local File Inclusion vulnerability in the WordPress plugin GeoDirectory up to and including version 2.8.187.\n- Unauthenticated attackers can include and execute arbitrary .php files because the geodir_basic_nonce nonce is available on every public frontend page.\n- Severity HIGH 8.1 (CVSS v3.1) with high impact on confidentiality, integrity, and availability.",
- "
Vulnerability Summary
\nCVE-2026-104899 is a Local File Inclusion (LFI) vulnerability in the WordPress plugin GeoDirectory – WP Business Directory Plugin and Classified Listings Directory. According to the official description, all versions up to and including 2.8.187 are vulnerable through the design_type parameter.
Unauthenticated attackers can include and execute arbitrary .php files on the server. The required nonce, geodir_basic_nonce, is available to any anonymous visitor because it is localized to every public frontend page via the geodir_params script object. This means no authentication, user interaction, or specific site content is needed to exploit this vulnerability.
Severity: HIGH 8.1 (CVSS v3.1) with vector CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H. CWE category: CWE-98.
Technical Impact
\nThis vulnerability allows local .php files to be included and executed. The impact includes execution of any PHP code contained within those files. An attacker can exploit it to bypass access controls, obtain sensitive data, or achieve code execution if a .php file can be uploaded and included.
The CVSS vector indicates high impact on confidentiality, integrity, and availability (C:H/I:H/A:H). Although the AC:H value indicates high attack complexity, the combination of no authentication (PR:N) and no user interaction (UI:N) still makes it a serious risk.
Affected Products
\nThe affected product is the WordPress plugin from vendor paoltaia: GeoDirectory – WP Business Directory Plugin and Classified Listings Directory. Based on the CNA title, all versions up to and including 2.8.187 are affected.
\nThis vulnerability is unauthenticated. There is no need for a user account, specific role, or special content. Because the nonce is available on public frontend pages, the attack surface is broader for sites running this plugin.
\nContext and References
\nCVE publication: 2026-10-10T05:31:02.786Z. Official references include Wordfence Threat Intel, several code links in Plugins Trac, and the fix commit on GitHub AyeCode/geodirectory.
\nFrom a defense perspective, this vulnerability underscores the importance of patch management, restricting file execution in upload directories, and monitoring logs for unusual parameters or request patterns. Do not rely on a publicly exposed nonce as the sole security control.
", "Mitigation
- ": "- Immediately update the GeoDirectory plugin to a newer version once the vendor releases a fix. Monitor the official repository and the GitHub commit AyeCode/geodirectory (2357d640dad7973988742a6706b3a857b6b05d52) for patch availability.\n- If an update is not yet available, consider temporarily disabling the GeoDirectory plugin until a patch is applied.\n- Do not rely on the geodir_basic_nonce nonce as a security control because its value is available to any anonymous visitor on public frontend pages.\n- Implement WAF rules or access restrictions to detect and block suspicious requests exploiting the design_type parameter, and review server logs for signs of local file inclusion attempts.\n- Audit .php files that can be uploaded and called by the application; restrict write and execute permissions on upload directories.",
- "
Komentar
Posting Komentar