
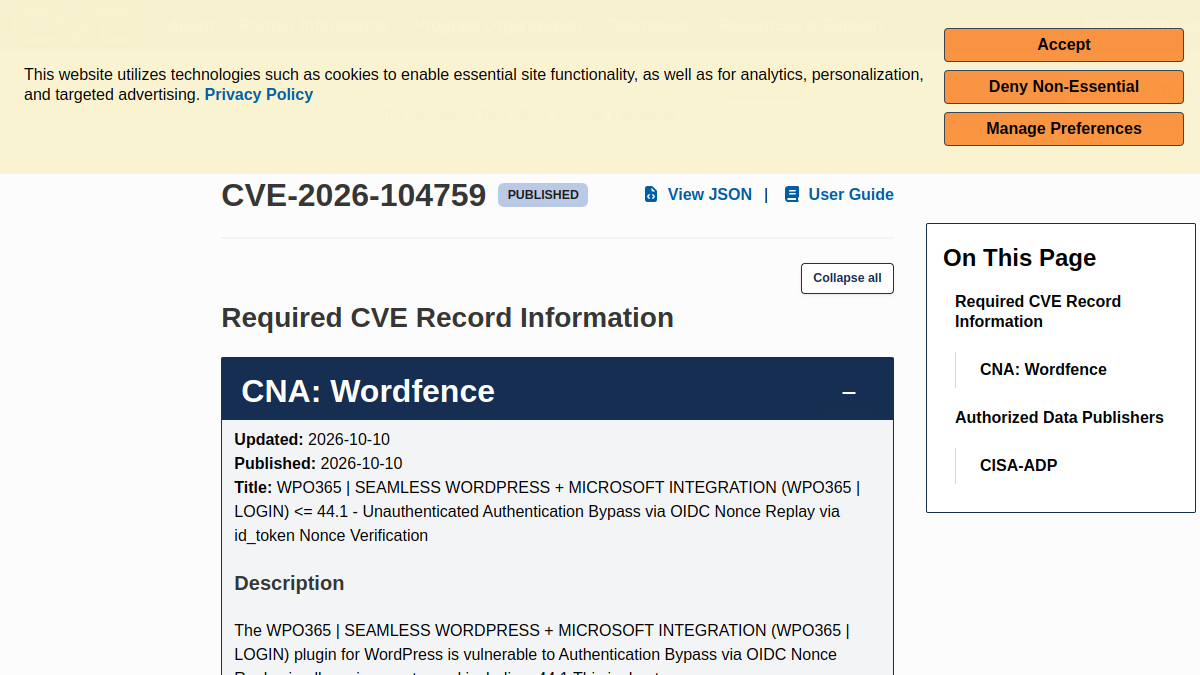
| CVE ID | CVE-2026-104759 |
| Severity | HIGH — CVSS CVSS V3.1 8.1 |
| Vector | CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H |
| CWE | CWE-287 CWE-287 Improper Authentication |
| Produk | wpo365 / WPO365 | SEAMLESS WORDPRESS + MICROSOFT INTEGRATION (WPO365 | LOGIN) — 0 (affected) |
| Dipublikasikan | 2026-10-10 |
Ringkasan Cepat
- CVE-2026-104759 adalah authentication bypass pada plugin WordPress WPO365 Login hingga versi 44.1 dengan severity HIGH 8.1 (CVSS V3.1).
- Penyebabnya pemeriksaan nonce OIDC yang gagal diam-diam karena wp_verify_nonce() dipakai untuk memvalidasi nonce 64 karakter hex dari Nonce_Service::create_nonce().
- Eksploitasi hanya aktif jika opsi use_id_token_parser_v2 diaktifkan; penyerang yang memiliki id_token valid pernah diterbitkan dapat replay dan berpotensi mengambil alih situs.
Ringkasan Kerentanan
CVE-2026-104759 adalah kerentanan Authentication Bypass via OIDC Nonce Replay pada plugin WordPress WPO365 | SEAMLESS WORDPRESS + MICROSOFT INTEGRATION (WPO365 | LOGIN). Deskripsi resmi menyatakan semua versi hingga dan termasuk 44.1 terdampak.
Kerentanan ini diberi severity HIGH 8.1 dengan vektor CVSS V3.1 CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H dan kategori CWE-287 Improper Authentication.
Menurut deskripsi, eksploitasi hanya mungkin ketika opsi plugin use_id_token_parser_v2 diaktifkan, karena konfigurasi itulah yang mengarahkan pemrosesan token ke parser deprecated yang memuat pemeriksaan nonce bermasalah.
Dampak Teknis
Akar masalah berada pada Id_Token_Service_Deprecated::process_openidconnect_token(). Fungsi ini memakai wp_verify_nonce() dari WordPress core untuk memvalidasi nonce yang dibuat oleh Nonce_Service::create_nonce(). Nonce tersebut berupa nilai hex 64 karakter, sementara wp_verify_nonce() tidak akan pernah berhasil memverifikasinya.
Akibatnya, pemeriksaan nonce gagal secara diam-diam tanpa menghentikan proses autentikasi. Eksekusi berlanjut ke authenticate_oidc_user() dengan id_token yang disuplai penyerang.
Penyerang tanpa autentikasi yang telah memperoleh id_token valid yang pernah diterbitkan untuk akun target dapat me-replay token tersebut dan terautentikasi sebagai pengguna WordPress mana pun, termasuk administrator. Dampak akhirnya adalah pengambilalihan situs secara penuh.
Produk Terdampak
Produk yang tercatat terdampak adalah WPO365 | SEAMLESS WORDPRESS + MICROSOFT INTEGRATION (WPO365 | LOGIN) dari vendor wpo365. Deskripsi resmi menyebut semua versi hingga dan termasuk 44.1 rentan.
Data kerentanan mencantumkan entri produk dengan versi 0 (affected) pada field versions. Untuk penilaian internal, utamakan deskripsi resmi: periksa apakah instalasi WordPress Anda memakai plugin ini pada versi 44.1 atau lebih lama.
Kerentanan ini tidak berlaku umum pada semua konfigurasi: hanya instalasi dengan opsi use_id_token_parser_v2 aktif yang berada pada jalur rentan yang dijelaskan.
Konteks dan Referensi
Publikasi CVE ini tercatat pada 2026-10-10T07:41:47.371Z. Referensi utama mencakup halaman Wordfence Threat Intel, beberapa file pada plugin Trac untuk tag 44.1, dan changeset 3727410 pada repositori plugin.
- Wordfence Threat Intel:
https://www.wordfence.com/threat-intel/vulnerabilities/id/aad7ddac-ed12-4263-8e68-64b1fca8dfad?source=cve - Plugin Trac 44.1:
Id_Token_Service_Deprecated.php,Router_Service.php,Id_Token_Service.php,Nonce_Service.php - Changeset:
https://plugins.trac.wordpress.org/changeset/3727410/wpo365-login
Dari perspektif pertahanan, prioritasnya adalah memastikan tidak ada instalasi yang tertinggal pada versi rentan dengan opsi parser v2 aktif, lalu mengikuti pembaruan resmi yang merujuk perubahan pada changeset tersebut.
Mitigasi dan Perbaikan
- Inventarisasi instalasi WordPress yang memakai plugin WPO365 Login versi 44.1 atau lebih lama, lalu tandai yang mengaktifkan opsi use_id_token_parser_v2.
- Terapkan pembaruan plugin yang tersedia dan merujuk changeset 3727410; uji login Microsoft/OIDC setelah pembaruan.
- Jika pembaruan belum dapat diterapkan, nonaktifkan sementara opsi use_id_token_parser_v2 karena jalur rentan hanya aktif saat opsi ini menyala. Pastikan dampak terhadap fungsi login dipahami dan diuji.
- Invalidasi atau revokasi id_token yang masih berlaku dan pertimbangkan rotasi kredensial integrasi OIDC jika ada indikasi penyalahgunaan.
- Audit log autentikasi untuk aktivitas mencurigakan, terutama login sebagai administrator, dan periksa akun pengguna yang tidak wajar.
Referensi Resmi
- CVE-2026-104759 — CVE Program (cve.org)
- https://www.wordfence.com/threat-intel/vulnerabilities/id/aad7ddac-ed12-4263-8e68-64b1fca8dfad?source=cve
- https://plugins.trac.wordpress.org/browser/wpo365-login/tags/44.1/Services/Id_Token_Service_Deprecated.php#L110
- https://plugins.trac.wordpress.org/browser/wpo365-login/tags/44.1/Services/Router_Service.php#L275
- https://plugins.trac.wordpress.org/browser/wpo365-login/tags/44.1/Services/Id_Token_Service.php#L107
- https://plugins.trac.wordpress.org/browser/wpo365-login/tags/44.1/Services/Nonce_Service.php#L72
- https://plugins.trac.wordpress.org/changeset/3727410/wpo365-login
Artikel ini disusun dari data publik CVE Program (cve.org). Selalu verifikasi patch resmi dari vendor sebelum menerapkan perubahan.
Pertanyaan yang Sering Diajukan (FAQ)
Apa itu CVE-2026-104759?
Versi WPO365 Login mana yang terdampak?
Apa penyebab teknisnya?
Kapan kerentanan ini dapat dieksploitasi?
Seberapa besar dampaknya?
Apakah sudah ada perbaikan?
English Version — CVE-2026-104759: WPO365 Authentication Bypass via OIDC Nonce Replay
Quick Summary
- CVE-2026-104759 is an authentication bypass in the WordPress WPO365 Login plugin up to version 44.1 with HIGH severity 8.1 (CVSS V3.1).
- The cause is a silently failing OIDC nonce check because wp_verify_nonce() is used to validate the 64-character hex nonce from Nonce_Service::create_nonce().
- Exploitation is only possible if the use_id_token_parser_v2 option is enabled; an attacker who has a valid previously issued id_token can replay it and potentially take over the site.
Vulnerability Summary
CVE-2026-104759 is an Authentication Bypass via OIDC Nonce Replay vulnerability in the WordPress plugin WPO365 | SEAMLESS WORDPRESS + MICROSOFT INTEGRATION (WPO365 | LOGIN). The official description states that all versions up to and including 44.1 are affected.
This vulnerability has been assigned severity HIGH 8.1 with the CVSS V3.1 vector CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H and category CWE-287 Improper Authentication.
According to the description, exploitation is only possible when the plugin option use_id_token_parser_v2 is enabled, because that configuration routes token processing to the deprecated parser that contains the flawed nonce check.
Technical Impact
The root cause lies in Id_Token_Service_Deprecated::process_openidconnect_token(). This function uses WordPress core's wp_verify_nonce() to validate the nonce created by Nonce_Service::create_nonce(). That nonce is a 64-character hex value, while wp_verify_nonce() will never successfully verify it.
As a result, the nonce check fails silently without stopping the authentication process. Execution continues to authenticate_oidc_user() with an id_token supplied by the attacker.
An unauthenticated attacker who has obtained a valid id_token that was previously issued for a target account can replay that token and authenticate as any WordPress user, including an administrator. The ultimate impact is full site takeover.
Affected Products
The product recorded as affected is WPO365 | SEAMLESS WORDPRESS + MICROSOFT INTEGRATION (WPO365 | LOGIN) from vendor wpo365. The official description states that all versions up to and including 44.1 are vulnerable.
The vulnerability data lists a product entry with version 0 (affected) in the versions field. For internal assessment, prioritize the official description: check whether your WordPress installation uses this plugin at version 44.1 or earlier.
This vulnerability does not apply to all configurations: only installations with the use_id_token_parser_v2 option enabled are on the vulnerable path described.
Context and References
The publication of this CVE was recorded on 2026-10-10T07:41:47.371Z. The main references include the Wordfence Threat Intel page, several files in the plugin Trac for the 44.1 tag, and changeset 3727410 in the plugin repository.
- Wordfence Threat Intel:
https://www.wordfence.com/threat-intel/vulnerabilities/id/aad7ddac-ed12-4263-8e68-64b1fca8dfad?source=cve - Plugin Trac 44.1:
Id_Token_Service_Deprecated.php,Router_Service.php,Id_Token_Service.php,Nonce_Service.php - Changeset:
https://plugins.trac.wordpress.org/changeset/3727410/wpo365-login
From a defensive perspective, the priority is to ensure that no installations remain on a vulnerable version with the parser v2 option enabled, then to follow the official update that references the changes in that changeset.
Mitigation
- Inventory WordPress installations that use the WPO365 Login plugin version 44.1 or earlier, then flag those with the use_id_token_parser_v2 option enabled.
- Apply the available plugin update that references changeset 3727410; test Microsoft/OIDC login after the update.
- If the update cannot yet be applied, temporarily disable the use_id_token_parser_v2 option because the vulnerable path is only active when this option is enabled. Ensure the impact on login functionality is understood and tested.
- Invalidate or revoke any still-valid id_tokens and consider rotating the OIDC integration credentials if there are signs of abuse.
- Audit authentication logs for suspicious activity, especially logins as administrator, and check for unusual user accounts.
Komentar
Posting Komentar